Fast Facts
VulnCheck published two critical advisories on November 12 covering the Copeland XWEB EVO vulnerabilities: a hardcoded administrator password and a predictable “code-of-the-day” password. Both give an unauthenticated network attacker administrator access, and the product line reached end of service in March 2026.
Operators of refrigeration and building monitoring should assume these units cannot be fixed and plan isolation first, replacement second. The checklist below turns that into five steps.
XWEB EVO is a web-based monitoring and control platform used with Dixell and Copeland refrigeration and HVAC equipment. The two Copeland XWEB EVO vulnerabilities were credited to researcher Valentin Lobstein (Chocapikk).
Fast Facts From the Advisories
- CVE-2026-124004, CVSS 9.3: a hardcoded Administrator credential lets an unauthenticated remote attacker take full admin control in a single request. Affects versions before 5.6.2. VulnCheck lists it in its KEV database.
- CVE-2026-124005, CVSS 9.2: the Administrator code-of-the-day password is derived from the device MAC address and date with no server-side secret, so valid credentials can be computed offline. Affects 4.3.0 through 5.8.8.
- VulnCheck states the product line reached end of service in March 2026. Its advisories do not confirm a fix for CVE-2026-124005.
“This product line reached it’s end of service date in March 2026.”VulnCheck advisory, Dixell/Copeland XWEB EVO
| Metric | Details |
|---|---|
| CVSS v4 Score | 9.3 – Hardcoded password flaw |
| CVSS v4 Score | 9.2 – Predictable password flaw |
| Highest Affected Version | 5.8.8 |
| End of Service | March 2026 |
| Source | VulnCheck advisories for CVE-2026-124004 and CVE-2026-124005, dated November 12, 2026. |
Why the Copeland XWEB EVO Vulnerabilities Are a Lifecycle Problem
A patch cannot rescue every critical bug. The affected range for the second flaw runs through 5.8.8, and the vendor line is out of support, so the realistic control is network isolation. This is the pattern we flagged earlier; see our analysis where we explain why most ICS advisories name no fix. The bill arrives later for anyone without a plan; see our analysis where we explain why device lifecycle management is IIoT’s coming bill.
Attack speed matters too. See our analysis where we explain how an AI-assisted OT attack moved from firewall to controller in 16 minutes. A single-request admin takeover is faster still, and similar post-patch exploitation hit other gateways; see our analysis where we explain Node-RED exploitation of Siemens IOT2050 gateways.
Vendors are also under rules now. See our analysis where we explain why most IIoT vendors are not ready for CRA reporting. If your estate includes retired product lines, the Copeland XWEB EVO vulnerabilities are a rehearsal for the same question across every unsupported gateway you own.
Copeland XWEB EVO Vulnerabilities: 5-Step Triage Checklist (copy-paste)
| Step | Action and parameter |
|---|---|
| 1. Inventory | List every XWEB EVO by site, firmware and MAC. Flag all versions from 4.3.0 up; treat anything not proven fixed as exposed. |
| 2. Remove exposure | Block inbound internet access to the web interface. Zero public IPs; confirm with an external scan. |
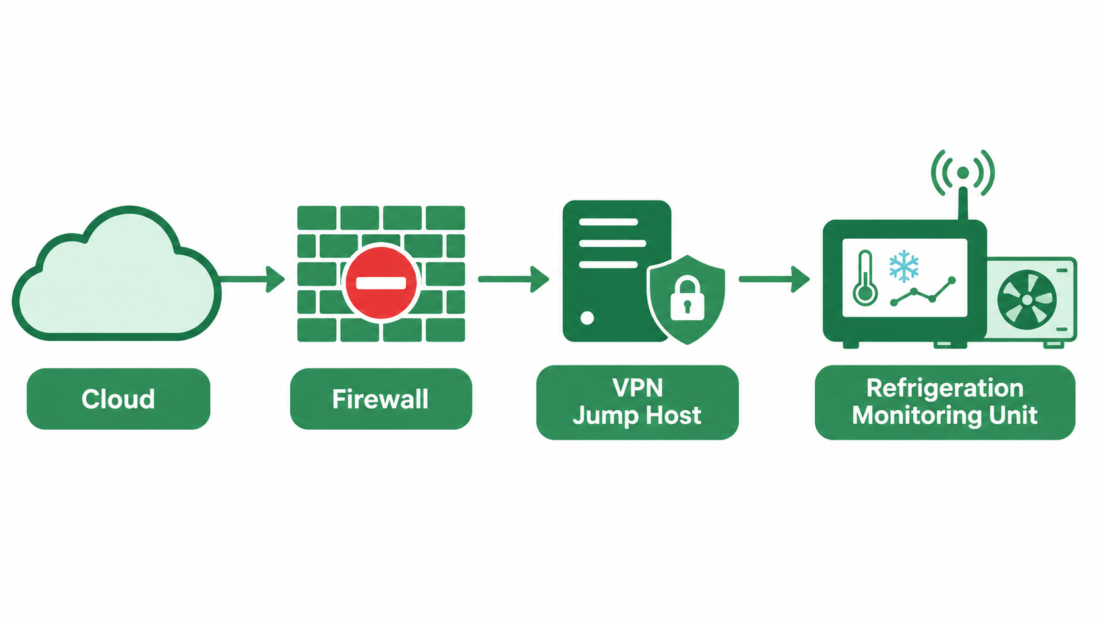
| 3. Restrict access | Allow only a VPN or a named jump host to reach the unit; deny all other source addresses at the firewall. |
| 4. Monitor | Alert on every Administrator login and any new user or config change; keep logs 90 days. |
| 5. Replace | Open a replacement ticket per unit with a target date within 90 days; ask the vendor in writing for a fixed version or end-of-life confirmation. |
⚠️ Hypothetical scenario: A Lagos cold-chain operator runs XWEB EVO units at six depots, reachable from the internet so engineers can check temperatures from home. After the Copeland XWEB EVO vulnerabilities go public, an attacker changes setpoints at one depot overnight. Spoiled stock costs more than the replacement controllers would have, and no one had a written exposure inventory.
💡 CreedTec Analyst’s Note by Daniel Ikechukwu
Strategic Impact
Whether these flaws were seen exploited is not stated in the advisories we read, so treat that as unknown. The safe assumption is that a one-request admin bypass will be tried quickly. Isolation costs hours; replacement needs budget, so start both clocks today.
Stop / Start / Watch
- Stop: leaving out-of-support controllers reachable from the internet.
- Start: keeping a firmware and end-of-support register per device.
- Watch: any vendor statement or CISA advisory on the Copeland XWEB EVO vulnerabilities.
ROI Outlook
Illustrative math: 10 units at USD 1,500 each is USD 15,000 to replace. One spoiled-stock event at USD 40,000 costs more than the whole refresh.
— Daniel Ikechukwu
Get the next playbook. One copy-paste OT security tool per issue, built for operators and security leads. Subscribe to the newsletter below.
For vendors: every operator reading about the Copeland XWEB EVO vulnerabilities needs asset discovery and remote-access control. If you sell OT asset inventory, secure remote access or OT firewalls, email creedtec@creedtec.online to sponsor the next edition.