Fast Facts
Notion confirmed that attackers who broke into AI inference vendor Fireworks AI reached chat transcripts from Notion’s AI Insights feature, linked to fewer than 1% of customer workspaces. The Notion Fireworks AI breach did not involve Notion’s own systems, according to Notion, and its customers are being told to treat the identified transcripts as exposed.
Most transcripts carry no user or workspace label, but anything typed into a chat can still identify a person or hold a secret. Notion has not said how many customers are affected, and the investigation remains open.
Companies now buy AI features that quietly pass their data to other companies. When one of those vendors is breached, the buyer finds out last. The Notion Fireworks AI breach shows how that chain works in practice, and which questions a contract should have settled beforehand.
How the Notion Fireworks AI Breach Unfolded
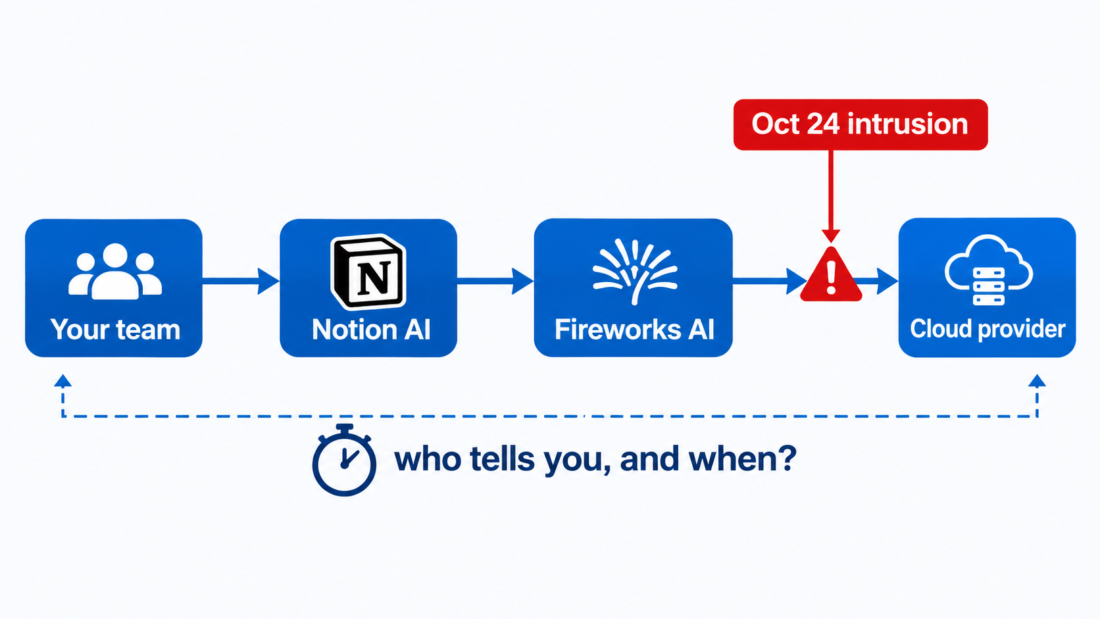
SecurityWeek reports Fireworks was breached twice in October. The second, on October 24, used an unauthorized workload on a third-party cloud provider that hosted Fireworks research machines; Fireworks contained it the same day. Fireworks alerted Notion on November 2, per both SecurityWeek and CybersecurityNews.
CybersecurityNews adds that Notion’s first review found only synthetic test data, and Notion disconnected from Fireworks and deleted its data there on November 3. Fireworks warned on November 6 that customer data may have been reached, and confirmed on November 8 that it included transcripts processed for Insights. The sources’ accounts of the first notice differ in emphasis, so read the dates as reported, not as an audited log.
| Stat | Detail |
|---|---|
| <1% | Notion workspaces linked to the exposed chat transcripts in the Notion Fireworks AI breach |
| 9 days | Time from the October 24 breach to the November 2 alert sent to Notion |
| 6 days | Time from the November 2 alert to the November 8 confirmation that transcripts were exposed |
Sources: SecurityWeek and CybersecurityNews (Nov 10 to 12, 2026). The day counts are CreedTec arithmetic from the reported dates.
What Was Actually Exposed
The data is AI chat transcripts processed for Insights, a feature that shows customers how they use AI. Notion says the transcripts contained no tool call results and mostly lacked author or workspace labels, calling them unattributable
. It also says no other feature was affected.
That label protects little. A pasted password, API key or customer name inside the chat travels with the text. A news digest of TechCrunch’s November 12 report says Notion notified the issuers of exposed third-party API keys, and that Fireworks says its default zero-data-retention services were not affected. We could not open the TechCrunch original. Exposed keys also have a market: see our analysis where we explain how discounted AI API access works as a data leak, and how an AI notetaker breach exposed 181,874 meetings for six silent months.
The Chain Behind the Chat Box
Notion used Fireworks as a general inference provider for open-weight models. Fireworks ran on a cloud provider. A customer’s chat therefore crossed at least three companies, and the customer’s contract usually covers only the first. See our analysis where we explain six questions to ask any AI vendor, including who handles your data downstream.
Notion’s response to the Notion Fireworks AI breach is the part buyers can copy: it cut the vendor within a day of the first alert, deleted its data there, paused Insights and stopped serving its open-weight models through Fireworks. Weaker is the timing. Roughly nine days passed between the October 24 intrusion and the first alert to Notion. See our analysis where we explain the AI contract risk nobody negotiates.
The sources do not say whether the Notion traffic sat on a retention-enabled path. Fireworks’ statement that its zero-data-retention default was unaffected leaves a fair question: why did transcripts exist there at all? Ask that of your own vendors, and read our analysis where we explain the blind spots in AI agent security.
⚠️ Hypothetical scenario: A Lagos HR-software firm lets staff use an AI assistant inside its workspace tool. After a vendor notice, the security lead searches chat history and finds a developer pasted a payment API key into the assistant. She rotates the key within the hour, then asks the workspace vendor for its subprocessor list, retention settings and breach-notice deadline. The vendor answers only the first. She moves sensitive prompts to a tool with documented zero retention.
💡 CreedTec Analyst’s Note by Daniel Ikechukwu
Strategic Impact
The Notion Fireworks AI breach turns AI inference vendors into part of every software buyer’s attack surface. Risk now sits in subprocessors you did not choose and rarely audit.
Stop / Start / Watch
- Stop: pasting credentials or customer data into AI chat boxes and assuming labels protect them.
- Start: requesting subprocessor lists, retention terms and breach-notice deadlines in writing.
- Watch: Notion’s final affected-customer count, Fireworks’ completed investigation, and when Insights returns.
ROI Outlook
A key rotation costs an hour; a leaked key can cost far more. Budget for credential hygiene and vendor reviews before adding more AI features to your stack.
— Daniel Ikechukwu, CreedTec (AI Systems Analyst)
Using AI features inside your SaaS stack?
The CreedTec AI Systems Brief shows which vendor questions to settle before the next incident.
Subscribe to the AI Systems Brief