Fast Facts
The Equinor cyberattack, disclosed November 17, targets some of the Norwegian energy group’s IT systems. Equinor says there are no indications of data theft and that operations and production are unaffected. It has not said how the attackers got in, or whether operational technology was involved.
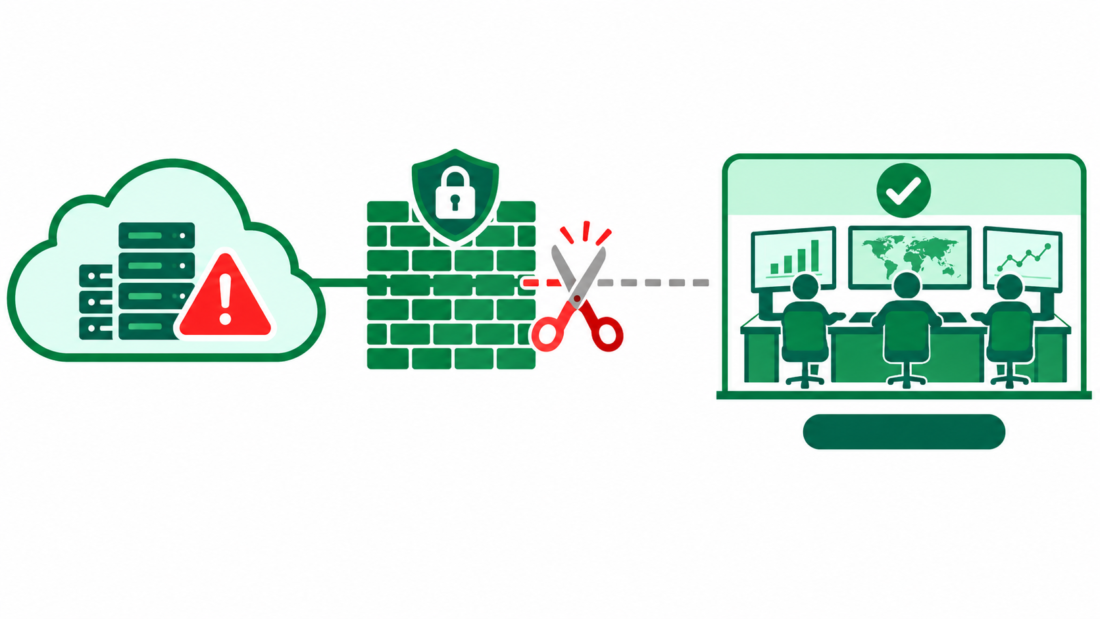
The lesson for plants is the split. When corporate IT is under attack, the question is whether control systems keep running on their own. The runbook below turns that into a drill with time limits you can test this quarter.
Reuters, as carried by Gulf News, reported that Equinor notified the relevant authorities and mobilised resources to restore integrity. A November 19 update, summarized by Security Boulevard’s OT news digest, said the Equinor cyberattack was still ongoing and production was normal.
Fast Facts From Equinor’s Statements
- Equinor detected an ongoing attack on certain IT systems; a spokesperson said internal applications and IT services could be disrupted.
- Norway’s National Security Authority and the petroleum safety regulator Havtil were notified, and the Police Security Service was informed, according to NRK.
- Unknown so far: when it began, the entry method, whether ransomware is involved, and whether control systems were touched.
“The attack has not affected Equinor’s operations and production.”Equinor statement, as quoted by IBTimes UK
| Metric | Details |
|---|---|
| Nov 17 | Equinor discloses the attack |
| 31% | Of EU gas imports came from Norway in 2025 |
| 54% | Of EU pipeline gas imports came from Norway |
| 3 | Norwegian authorities notified or informed |
Sources: Equinor statement via IBTimes UK; European Commission figures as cited by IBTimes UK.
What the Equinor Cyberattack Means for Your Plant
An IT-only incident can still stop a plant if production depends on IT services such as remote access, historians or licensing. The proof is a drill, not a diagram. Attackers can move quickly once inside; see our analysis where we explain how an AI-assisted OT attack went from firewall to controller in 16 minutes. Direct attacks on the floor are rising too; see our analysis where we explain why industrial cyberattacks target factory floors directly.
Certification does not prove separation. See our analysis where we explain what the IEC 62443 badge does and does not prove. Unsupported devices make isolation the only fix; see our analysis where we explain the Copeland XWEB EVO case with no patch path.
Connected devices also get pulled into botnets during incidents; see our analysis where we explain how to protect industrial IoT from botnet attacks. The Equinor cyberattack is a prompt to rehearse the cut-over before you need it.
Equinor Cyberattack Lesson: IT-Down, OT-Up Runbook (copy-paste)
Suggested time limits. Test in a maintenance window first.
| Step | Action and parameter |
|---|---|
| 1. Declare | Incident lead calls “IT-down” and starts the log. Target: under [10] minutes from first alert. |
| 2. Cut the conduit | Disable remote access and the IT-to-OT firewall rules. Target: under [15] minutes, tested by two people. |
| 3. Confirm OT autonomy | Check that control, safety and alarm functions run without IT services, directory logins or internet. Record any dependency found. |
| 4. Protect evidence | Copy OT logs and historian data to offline media before any restore. |
| 5. Manual mode | List processes that can run manually for [8] hours, with named operators and printed procedures. |
| 6. Restore rule | Reconnect only after IT is verified clean, one conduit at a time, with approval from the plant manager. |
Score: any step that misses its time limit, or any OT function that needed IT, becomes a ticket with an owner and a date.
⚠️ Hypothetical scenario: A Lagos oil services firm learns of the Equinor cyberattack and assumes its own control rooms are safe because they sit on a separate network. During a drill, the team finds the alarm system authenticates against a corporate server. With that server offline, operators lose alarms. A planned test found it; a real attack would have exposed it during production.
💡 CreedTec Analyst’s Note by Daniel Ikechukwu
Strategic Impact
Equinor’s own statements are the evidence so far, and they say production is unaffected. That is reassuring but unproven from outside. The useful move for operators is to assume the same could happen to them and to measure how long their cut-over takes.
Stop / Start / Watch
- Stop: assuming a separate network means separate dependencies.
- Start: running a timed IT-down drill every quarter.
- Watch: Equinor’s follow-up on entry method, ransomware and any OT involvement in the Equinor cyberattack.
ROI Outlook
Illustrative math: a plant earning USD 50,000 an hour that loses eight hours to an avoidable IT dependency forgoes USD 400,000. A drill that finds it costs a few engineer days.
— Daniel Ikechukwu
Get the next playbook. One copy-paste OT security tool per issue, built for operators and security leads. Subscribe to the newsletter below.
For vendors: every operator following the Equinor cyberattack will ask how to prove IT and OT separation. If you sell OT network segmentation, industrial firewalls or secure remote access, email creedtec@creedtec.online to sponsor the next edition.